 Attestorian
Make every AI action tamper-evident.
Seal turns each step an agent takes into evidence that cannot be quietly changed. Alter one character, remove a step, or slip in an extra one, and verification fails.
From a single step to a sealed package.
Capture
Inputs, policy checks, tool calls, results, and outputs are recorded as they happen.
Chain
Each step is linked to the one before it, so order and completeness are part of the record.
Sign
The chain is digitally signed with keys you control, held in your KMS or HSM.
Package
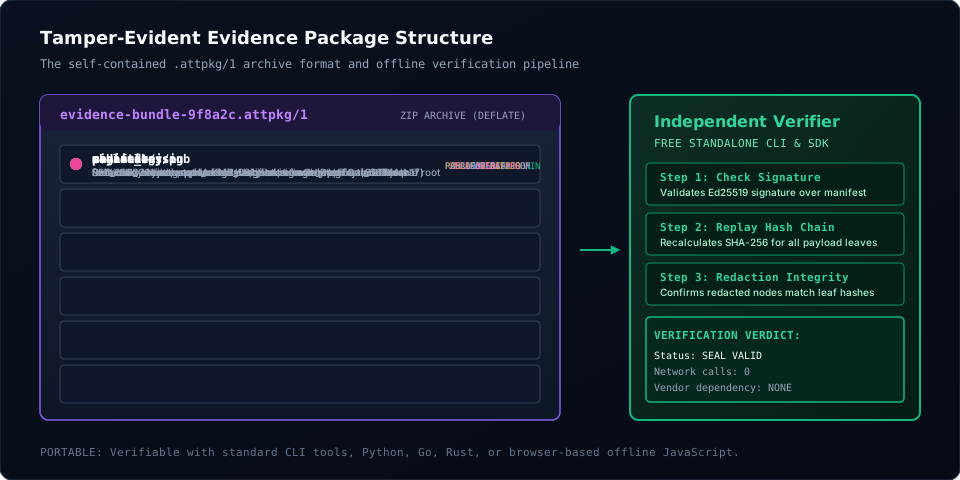
A compact, portable evidence package that any verifier can check.
Change one character. Watch the seal break.
Live tamper demo: a sealed AI wire settlement
Edit any value below. Even a single character breaks the seal.
Evidence that holds up.
- Detection of any edit, deletion, reordering, or insertion
- Customer-held signing keys through your KMS or HSM
- Industry-standard, publicly reviewed algorithms in the production core
- Fail-closed verification: inconsistencies never produce a partial pass
- Independent verifiers in different programming languages that must agree on a shared test corpus
- Model, prompt, and tool version lineage recorded with each action
What a seal proves, and what it does not. A valid seal proves the record has not changed since it was sealed and identifies who sealed it. It does not by itself prove that a compromised system recorded truthfully, that capture was complete outside instrumented paths, or that an AI answer was correct. We address these limits with capture-completeness declarations, trusted time-stamping and witnessing options, and human approvals.
Next
Need to share evidence externally? Redact hides sensitive fields while the seal stays valid.
Frequently asked questions
How does Attestorian Seal prevent privileged insiders from altering AI logs?
Attestorian Seal links every AI step to the previous step's cryptographic digest and signs the resulting chain using private keys stored inside your KMS or HSM. Modifying a single character, deleting an entry, reordering steps, or inserting an extra instruction invalidates the root signature during verification.
Who holds the cryptographic signing keys for Attestorian Seal?
Your organization retains exclusive custody of all signing keys inside your existing Key Management Service (KMS) or Hardware Security Module (HSM). Attestorian never holds your private signing keys, ensuring sovereign cryptographic proof for regulators and external auditors.
Seal your AI agent audit trails.
Protect your autonomous AI systems with tamper-evident cryptographic packaging. The USD 10,000 pilot fee is credited in full toward your annual license.
Last updated: